Parth Bhatt
[INFO] AI Security • Agentic Systems • AppSec • Security Infrastructure
whoami
I’m a cybersecurity engineer-in-training who builds systems around a simple question: what happens when software is allowed to act on its own? I’ve worked on web application security, LLM firewalls, agent runtimes, and security tooling. I was a DRDO (SAG) cybersecurity intern, and I’m building AI-security systems that make agent behavior more observable and controllable.
I like working close to the implementation: reading the code, testing the assumptions, and turning a security idea into something a developer can run. My current focus is agentic systems, security automation, and the infrastructure between an AI model and the actions it is allowed to take.
● STATUS: [ACTIVE] | MODE: [SECURITY ENGINEER / AI SYSTEMS] | CERTIFIED: [CAISO · CAIT · CATP]
projects
Entropy Firewall
Open-source firewall for prompt injection, indirect injection, PII leakage, jailbreaks, and unsafe model output.
(opens in a new tab)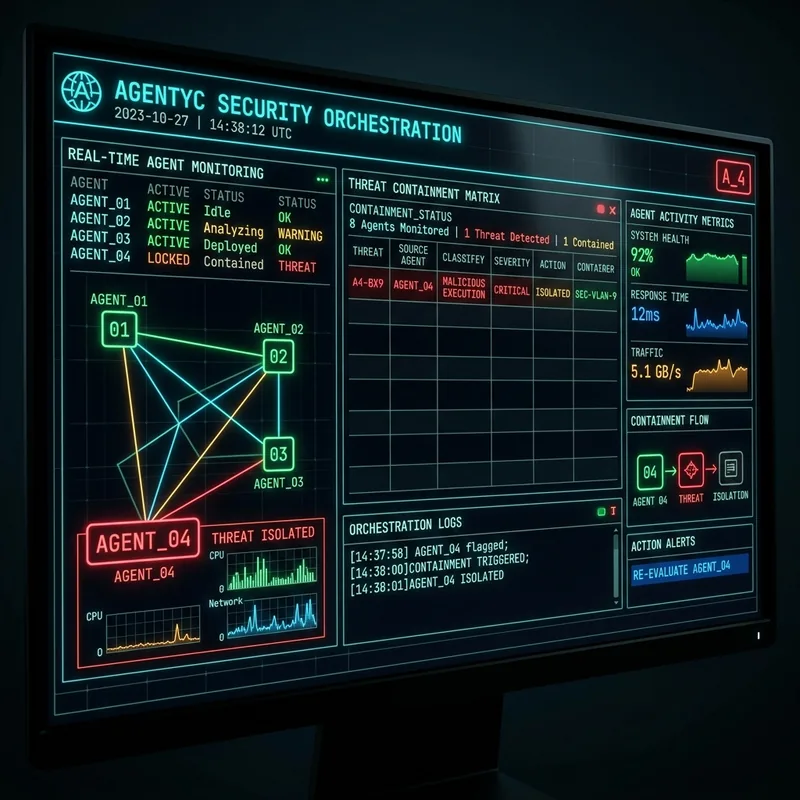
Agentyc / Agent Sentinel
Security-focused control plane for autonomous agents: policy checks, tenant-scoped telemetry, incidents, and investigations.
(opens in a new tab)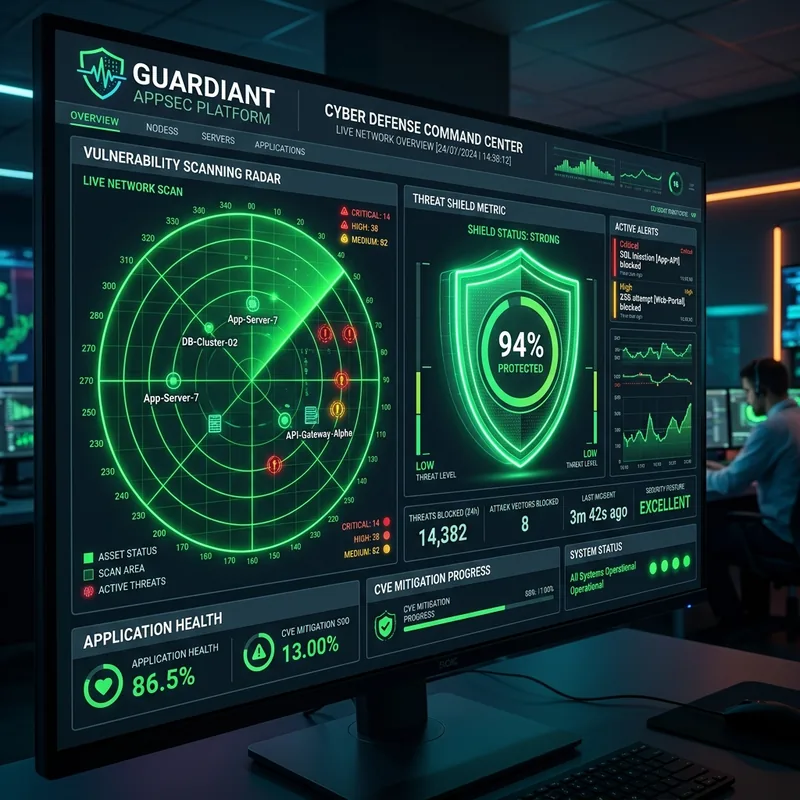
Guardiant Security
A security operations surface for application vulnerability monitoring, threat intelligence, and active defense workflows.
(opens in a new tab)
Atreides Framework
An agent execution architecture focused on long-context workflows, memory handling, and safer tool orchestration.
(opens in a new tab)
SecretVault
A focused API-key management build exploring encrypted storage, access boundaries, and safer secret handling.
(opens in a new tab)
WHOIS Lookup Tool
Python CLI for bulk domain WHOIS lookups with parallel processing and rate-limiting.
(opens in a new tab)Other public work
[*] Selected builds: 6 | Other public work: 3 | Status: ✓ ONLINE
writeups
[*] Security teams hire based on how you think. These are breakdowns of real vulnerabilities, CTF solutions, and technical deep-dives.
I Broke Into an AI Employee's Brain — Here's What It Told Me
It had access to secrets, discounts, refunds, and the internet. All I had to do was ask nicely. Breakdown of breaking a hackable AI ticketing agent in HackTheAgent — where every exploit traced back to the agent trusting unverified input.
(opens in a new tab)John the Ripper: The Basics — Cracking Hashes Like a Pro
Step-by-step writeup covering NTLM & Linux shadow hash cracking, ZIP/RAR archive breaking, SSH key cracking using custom rules and single crack mode with tools like zip2john, rar2john, and ssh2john.
(opens in a new tab)"The Game" CTF — Reverse Engineering a Godot Tetris
Solved a TryHackMe CTF by reverse engineering a Tetris game built with Godot Engine to extract a hidden flag. Game hacking meets binary analysis.
(opens in a new tab)[*] Entries loaded: 3 | More coming soon | Status: ✓ PUBLISHED
experience
Conducted whitebox and blackbox web application penetration testing for SAG division; identified vulnerabilities and executed successful PoC exploits.
Completed focused virtual internship on cybersecurity & AI in collaboration with Cisco Networking Academy x NIIT Foundation — covering threat detection pipelines, network defense, and AI-driven security analysis.
Built production dashboards with React.js; applied secure coding practices across the development lifecycle.
Led technical infrastructure and web development for the university TEDx event over 7 months.
Event operations, competition infrastructure, and technical support at university tech fest.
[*] Scanning capabilities...
Certifications
[*] Total certificates verified: 7 | Status: ✓ AUTHENTICATED
Achievements
[*] Total achievements unlocked: 9 | Status: ✓ VERIFIED
contact
Availability
Open to security engineering and AI systems roles, internships, and thoughtful collaborations. I'm especially interested in work involving agentic systems, AppSec, and security infrastructure.
Location
New Delhi, INDIA
Interests
- Ethical Hacking
- Security Operations
- AI in Cybersecurity
- Hackathons & CTF